

The dangers of using the same password across multiple accounts
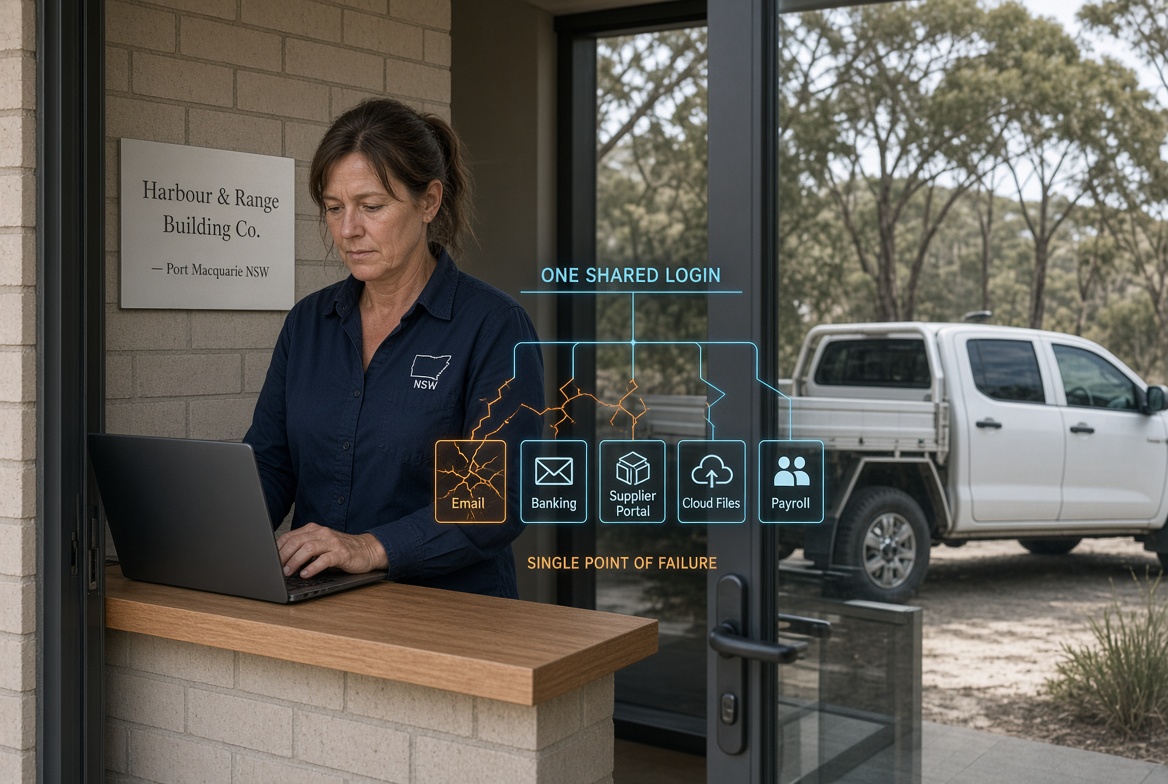
Many people choose one easy login credential and apply it everywhere. The habit feels convenient. Yet it creates a single point of failure that criminals actively exploit. Everyday users and decision makers in smaller operations often underestimate how quickly one leaked credential can open multiple doors. Local operators throughout the New South Wales mid-north coastal district face the same exposure as anyone else.
Alterations in how access is managed
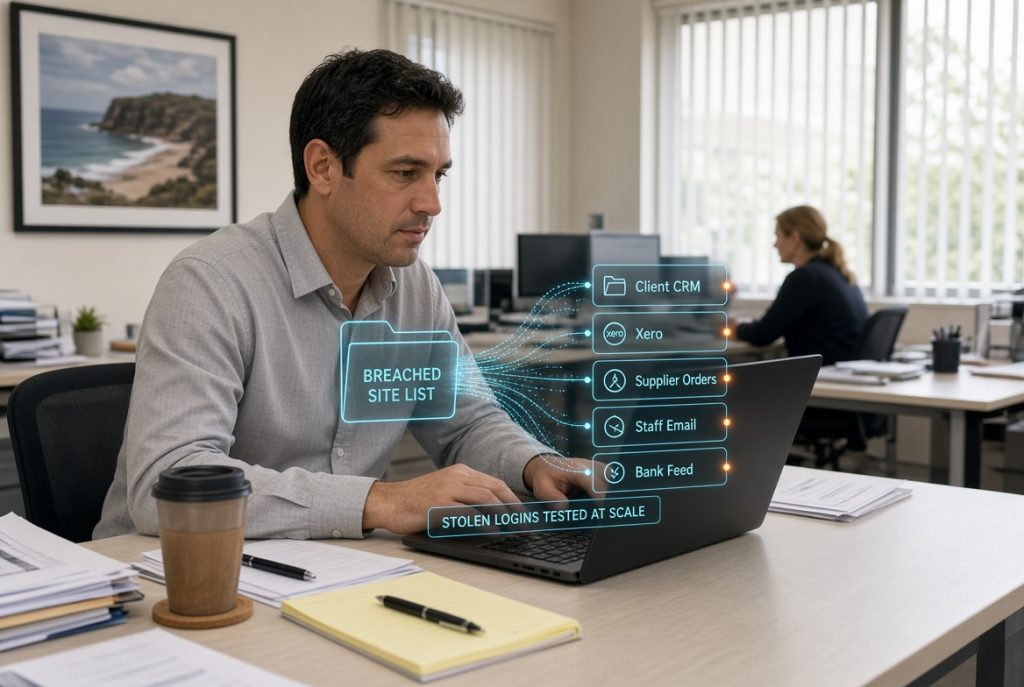
Online services now store everything from client lists to financial records. Each new platform adds another place that needs a credential. When the same one is reused, a breach at any single site can cascade. Attackers collect these leaked credentials and test them automatically across other services.
Reasons the practice creates problems
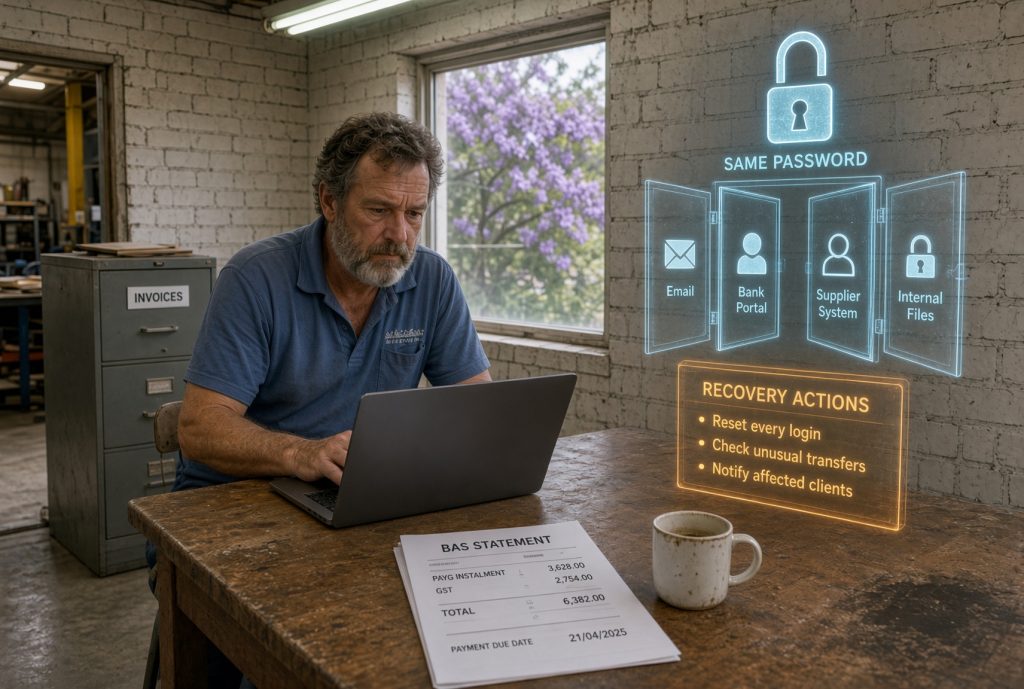
One compromised credential can grant entry to email, banking portals, supplier systems and internal files. The recovery process then involves changing multiple logins, checking for unauthorised activity and restoring trust with clients. Decision makers who continue the habit accept higher odds of this chain starting.
Clear explanations of central ideas
These ideas become practical once linked to the actual platforms a business already uses each day.
Credential reuse means applying the identical login secret to more than one service.
A credential stuffing attack occurs when stolen lists are tested at scale against other sites.
Unique credentials ensure that a problem at one service stays contained.
Approaches suited to different workplaces
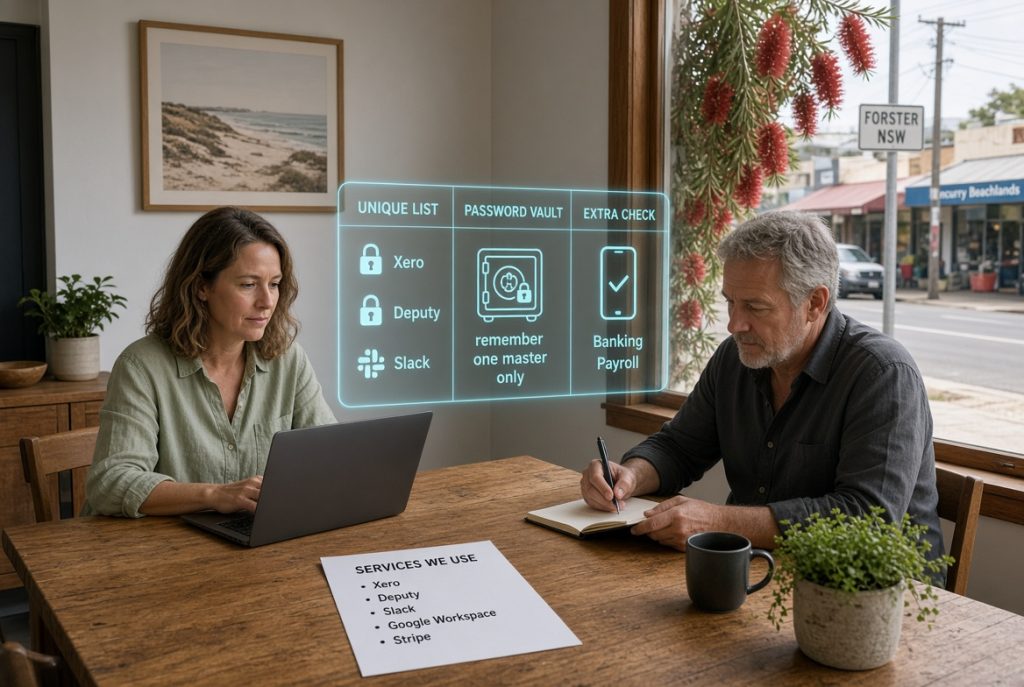
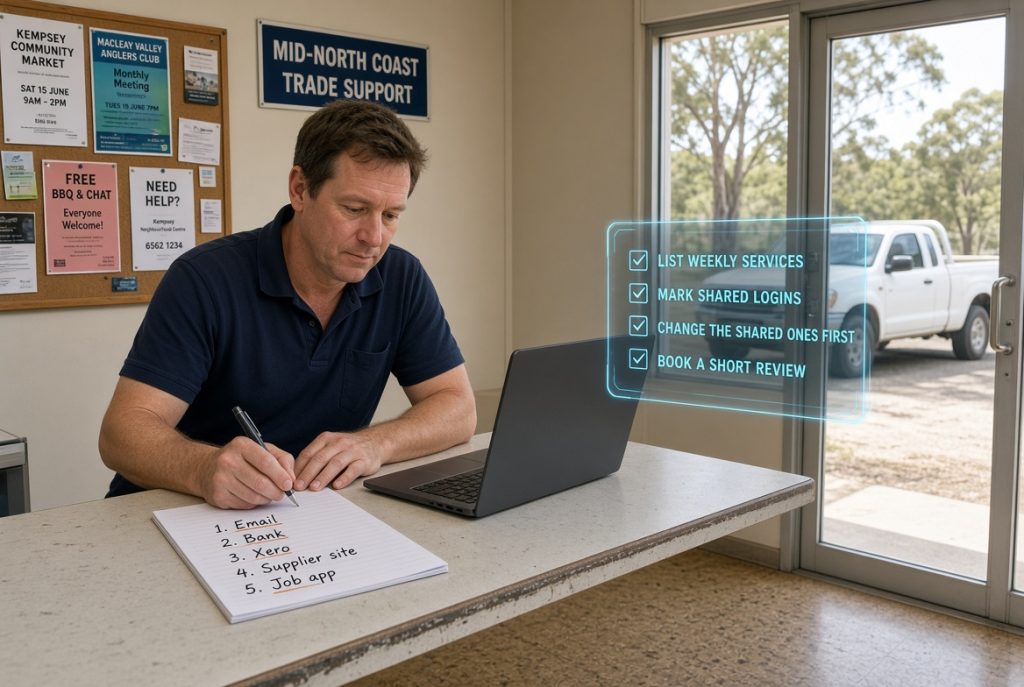
Some operations start by listing every service that holds important information and assigning a distinct credential to each. Others introduce a trusted password manager, so people no longer need to remember complex strings. A few add extra verification steps on the most sensitive accounts. The useful approach depends on the number of platforms in daily use and the sensitivity of the information they hold.
Consequences for the organisation
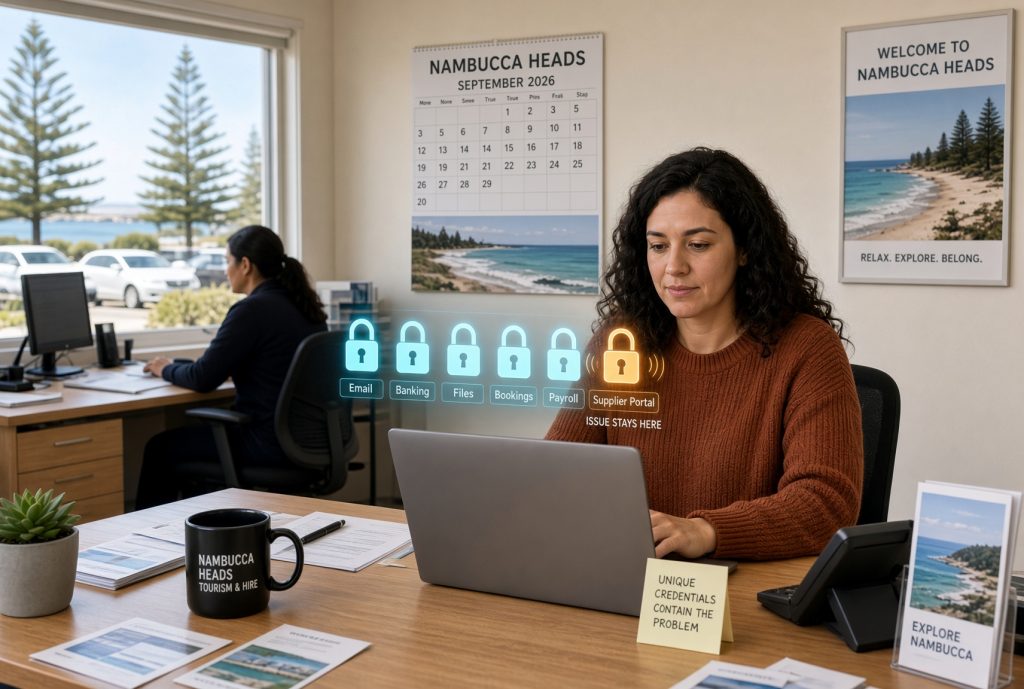
When credentials stay unique, a problem at one service remains limited. Files, messages and financial access stay better protected. Decision makers spend less time on emergency changes and more time on normal work. Client confidence remains higher because the chance of wide exposure drops.
Help supplied by PC Pitstop
PC Pitstop assists local operators with practical ways to move away from repeated credentials. We focus on clear steps and tools that fit the pace of smaller operations. Support covers both the initial change and the habits that keep the improvement in place.
Still using one credential for everything?
Drop into our store and talk with us about Technology Consulting. We will review the platforms you rely on and show straightforward ways to assign unique credentials and manage them without daily friction. One visit gives you a clear, practical plan ready to put into action.